AI penetration test: get attacked before others do it for real.
Attackers use AI to scan websites for vulnerabilities automatically. We turn this around: our AI agents attack your website, shop or web application in a controlled way, with your written authorization. We confirm every finding manually and document it with proof, a rating and a fix.
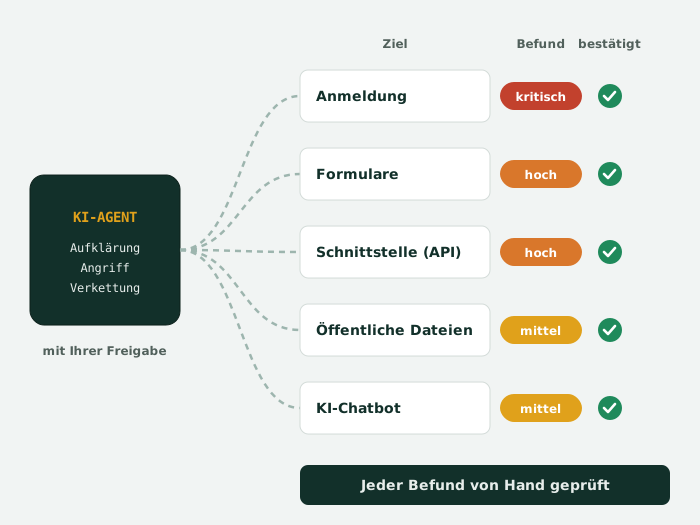
What we actually do
How an AI attack simulation works, from authorization to retest.
- Define scope and rules in writing: systems, time window, user roles, limits
- Reconnaissance by AI agents: everything an attacker can find out about your systems from the outside
- Automated attacks in thousands of variants on login, forms, interfaces and business logic
- Chaining small weaknesses into real attack paths, as an experienced attacker would
- Manual confirmation of every finding by us, so the report contains no false positives
- Report with proof, rating by urgency and a concrete fix for each finding
- Retest after fixing; on request, we implement the measures
What the AI agents attack
| Reconnaissance | Subdomains, open services, software and versions in use, forgotten test and admin pages, publicly accessible backups, .git and .env files. |
| Login and permissions | Password guessing, login bypass, sessions and cookies, access to other users' data via modified URLs or IDs, privilege escalation between user roles. |
| Inputs and forms | SQL injection, cross-site scripting, command injection, file uploads with malicious code, misuse of contact forms for spam and phishing. |
| Interfaces (API) | Missing permission and input checks, too much data returned, missing rate limiting, keys in the source code. |
| Business logic | Manipulating prices, vouchers and quantities, bypassing order flows, skipping payment steps. |
| AI features | Chatbots and AI assistants: prompt injection, leakage of internal data, unauthorized actions via connected tools. |
| Server and software | Known vulnerabilities in PHP, CMS, plugins and libraries (e.g. PHP2Shell, wp2shell), insecure configuration, missing security headers. |
How the test stays safe
- Only when commissioned in writing by the operator, with defined systems, time window and limits
- Preferably on a test copy; on live systems only with care and by agreement
- No load attacks, no deletion, no extraction of data beyond what proof requires
- Hosting provider and agency informed in advance on request
- Immediate phone call and test halted if a critical issue is found
- All test data is deleted on completion
Prices and scope of services
Guide prices net, plus statutory VAT. The fixed price in our written quote is binding.
| AI attack simulation, website or shop One domain with CMS or shop, public areas and customer account, report and retest | €1,490–3,900 |
| AI attack simulation, web application Several user roles, interfaces (API), business logic, AI features | from €3,900 |
| Retest after fixing All critical and high findings checked again | included |
| Fixing the findings Or fixed price after the report | €45–60 / hour |
What you get
Our approach
- AuthorizationScope, time window and limits in writing.
- ReconnaissanceAI agents map the attack surface.
- AttackControlled attacks, continuously monitored.
- ReportFindings confirmed, rated, with a fix.
- RetestFixes checked again.
Frequently asked questions
What is the difference from the security audit?
The audit checks configuration, software versions and known vulnerabilities. The AI attack simulation goes further: AI agents behave like an attacker, chain small weaknesses into a real attack path and check whether a vulnerability can actually be exploited. We confirm every finding manually.
Is this dangerous for our ongoing operations?
No, if it is properly planned. We prefer to test on a test copy, set time windows and limits in writing and refrain from load attacks and from deleting or extracting data. If we find a critical issue, we stop and call you immediately.
Why AI?
Attackers already use AI to scan websites for vulnerabilities, both at scale and in a targeted way. Using the same methods, we find gaps faster and more thoroughly than with tools that only check for known patterns. The assessment and recommendations come from people.
Do you also test our AI chatbot?
Yes. Chatbots and AI features on websites can often be manipulated through crafted inputs into revealing internal data or performing actions (prompt injection). This is a separate test area of the attack simulation.
Is the report recognized for certifications?
For ISO 27001, TISAX or insurance requirements, we clarify with you in advance what is required of the test report. The attack simulation does not replace a formal test by an accredited auditor.
What does the AI attack simulation cost?
For a website or shop €1,490–3,900 net, for a web application with APIs and several user roles from €3,900. The retest after fixing is included. We quote the fixed price once the scope is defined.
Request an attack simulation
Tell us the address of your website or application, the system and whether there are customer accounts or APIs. You will receive a proposal for scope and fixed price.
By phone: 030 417 17370
Briefly describe what you have in mind. We will get back to you with a concrete assessment.
Danziger Straße 78a
10405 Berlin
Berlin-Prenzlauer Berg