Website security check: a full audit with a clear report.
We systematically check your website, shop or web application for vulnerabilities: software versions, server configuration, access, forms and data backup. You receive a report with an assessment by urgency and concrete measures, understandable for management and technical staff.
What we check
Based on the recommendations of the BSI and the OWASP Top 10.
- PHP, CMS, plugin and library versions against known security vulnerabilities (CVE)
- Server and hosting: file permissions, executable files in upload folders, open directories
- TLS certificate, encryption and security headers such as HSTS and Content-Security-Policy
- Publicly accessible files: backups, .git and .env files, log files, test pages
- Access: admin area, password rules, two-factor login, orphaned accounts
- Forms, uploads and interfaces: input validation, spam and abuse protection
- Searching for traces: web shells, foreign files, hidden redirects, new administrators
- Data backup: in place, stored separately, restore tested
- Embedded external services and unintended data leakage
Your report: clearly sorted by urgency
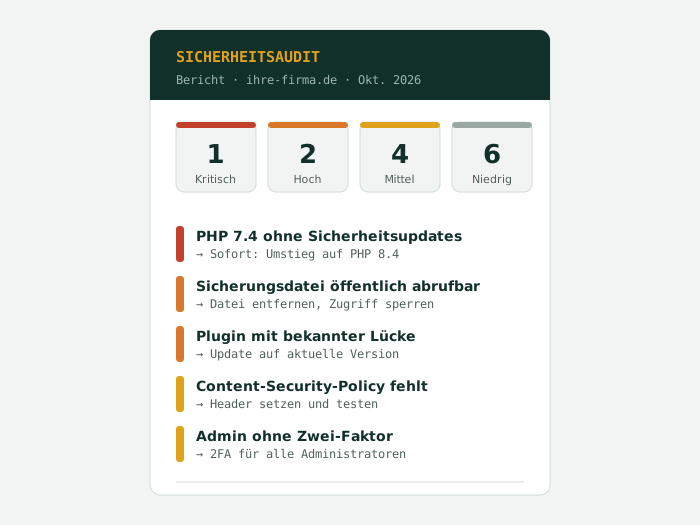
| Critical | Act immediately: vulnerability is already being exploited or is reachable without logging in |
| High | Fix soon: e.g. outdated software with a known vulnerability, exposed backup files |
| Medium | Fix as planned: e.g. missing security headers, weak password rules |
| Low | Improve when convenient: e.g. unnecessary information in error messages |
For each point: what was found, why it is a risk, how it is fixed and how much effort it takes.
Prices and scope of services
Guide prices net, plus statutory VAT. The fixed price in our written quote is binding.
| Compact security check One website with CMS, external check and check in the hosting, report with measures | €390–690 |
| Comprehensive security audit Shop or web application with server, interfaces and access, detailed report | €900–2,500 |
| Re-check of the critical points After the measures have been implemented | included |
| Implementation of the measures Or fixed price after the report | €45–60 / hour |
Why an audit
Our approach
- EngagementDefine the scope, written authorisation from the site operator.
- AuditNon-intrusive, without disrupting operations.
- ReportFindings by urgency, with measures.
- ImplementationBy you, with your agency or with us.
- Re-checkCritical points checked again.
Frequently asked questions
What exactly do you check in the security check?
Software versions of PHP, CMS and extensions, the server configuration, certificate and security headers, publicly accessible files such as backups or configuration files, access and password rules, forms and uploads, traces of an attack, and the data backup. The exact scope is set out in the quote.
Is this a penetration test?
No. Our audit systematically checks configuration, software versions and known vulnerabilities, non-intrusively and without disrupting operations. It does not replace a formal penetration test, for example for certifications. We will tell you when such a test makes sense.
Do you need access credentials?
For the compact check, an external view is often enough. For a full audit we need read access to hosting and CMS. When we are finished, you revoke our access again, which we expressly recommend.
Does the audit help with GDPR?
Yes, as evidence of appropriate technical measures under Art. 32 GDPR. It does not replace a legal assessment.
What happens after the report?
You decide which measures to implement, yourself, with your agency or with us. After implementation we re-check the critical points; this re-check is included in the price.
Request a security check
Tell us your website address, the system and whether it is a website, shop or web application. You will receive a fixed price.
By phone: 030 417 17370
Briefly describe what you have in mind. We will get back to you with a concrete assessment.
Danziger Straße 78a
10405 Berlin
Berlin-Prenzlauer Berg