Web security for businesses: close vulnerabilities before others find them.
Websites, shops and web applications are attacked automatically every day. We check your website, bring PHP and your CMS up to a secure level, clean up after an attack and keep everything up to date. From our workshop in Berlin-Prenzlauer Berg.
Our services for your web security
PHP2Shell and PHP update
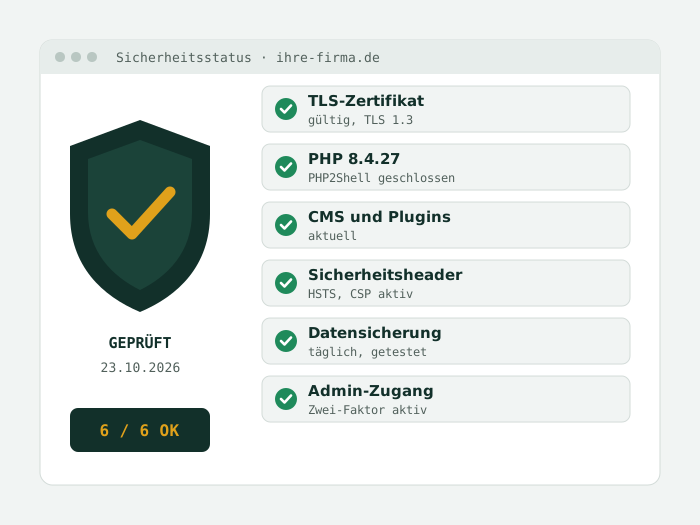
Critical vulnerability in PHP: check version, update, adapt code.
MoreAuditSecurity audit for websites
Full audit with a report by urgency and measures.
MoreWordPressWordPress security
Protection against wp2shell, updates, hardening and maintenance.
MoreEmergencyWebsite hacked?
Remove malicious code, close the vulnerability, restore the website.
MoreGDPRBFSG and GDPR
Cookies, privacy and accessibility implemented technically.
MorePricesPrices and support
Security check, audit and website care from €99 / month.
MoreCritical vulnerability in PHP: check your version now
On 21 October 2026 the PHP team closed two critical security vulnerabilities (CVE-2026-109618 and CVE-2026-109619, rated 9.2 out of 10). They allow program code to be executed on the web server without logging in. Affected are websites and shops running an older PHP version, whether WordPress, Shopware, Joomla or custom software.
- Safe versions are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 or newer
- PHP 7.x, 8.0 and 8.1 no longer receive updates from php.net
- First attacks have already been observed
- Updating WordPress or the shop alone is not enough, the vulnerability is in PHP itself
How we work
Security requires care and clear rules. We only check systems for which the operator has commissioned us in writing, and we do not attack anything in a way that disrupts ongoing operations.
- Backup before every intervention, restore tested
- Changes first in a test copy, then on the live site
- Report understandable for management and technical staff
- Every change documented, access handed back on completion
- Based on the recommendations of the BSI and the OWASP Top 10
Frequently asked questions
Is my small company website even a target?
Yes. Attacks are almost always automated: programs scan the internet for known vulnerabilities in PHP, WordPress or shop software and attack every matching site, regardless of the size of the company. Hijacked websites are used for spam, phishing or as a springboard for further attacks.
My hosting provider does the updates. Isn't that enough?
Usually the hosting provider only updates the server packages. Whether your website really uses the new PHP version, whether the CMS, plugins and custom code are up to date, and whether someone got in before the update are things they generally do not check.
What does a security check cost?
A compact security check of a website costs €390–690 net, a comprehensive audit for a shop or web application €900–2,500. The PHP2Shell quick check with update costs €149–349. We state the fixed price in advance.
Do you work with our hosting provider or our agency?
Yes. We work with Plesk, cPanel and our own servers and coordinate any work with the hosting provider or agency. You keep all access credentials, and we document every change.
Request a security check
Tell us your website address and the system (e.g. WordPress, Shopware, custom software). We will get back to you with an assessment and a fixed price.
By phone: 030 417 17370
Briefly describe what you have in mind. We will get back to you with a concrete assessment.
Danziger Straße 78a
10405 Berlin
Berlin-Prenzlauer Berg